


Static, local analysis
It detects risky patterns and configuration gaps, not live account activity.
Audit pasted code, provider restrictions and budget controls entirely in your browser. Get a prioritized containment plan in under a minute.
THE PROBLEM
Developers repeatedly report missing spend ceilings, browser-exposed keys and service-account abuse. Native controls are improving, but they differ by provider and can still leave gaps.
Check public prefixes, client bundles, project limits and alert-only assumptions.
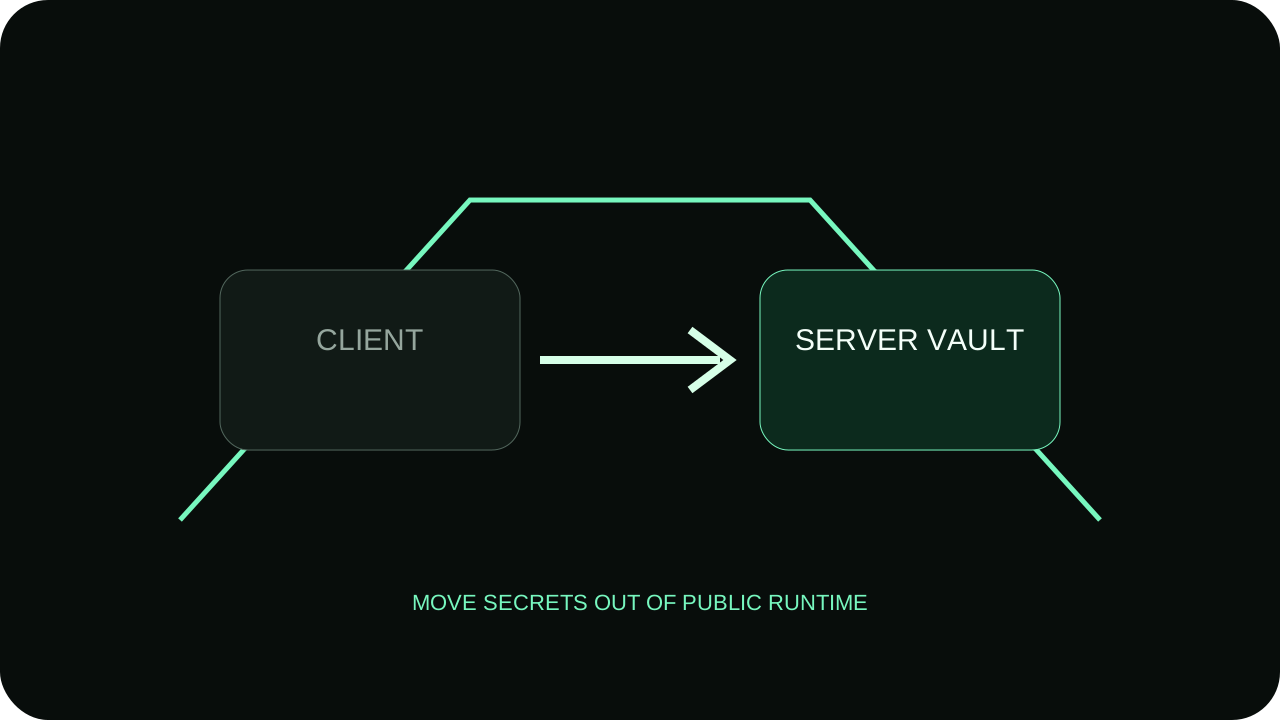
Spot exposed secret formats, local storage and unbounded development workflows.
Review key restrictions, legacy Firebase exposure and residual service-account risk.
FREE LOCAL DIAGNOSTIC
Paste only code or configuration you are allowed to inspect. Analysis happens locally in this tab; nothing is transmitted.
CONTAINMENT, NOT PANIC
A useful response is ordered: stop exposure, remove old credentials, enforce provider restrictions, test the ceiling, then preserve an audit trail.
BUDGET BUFFER
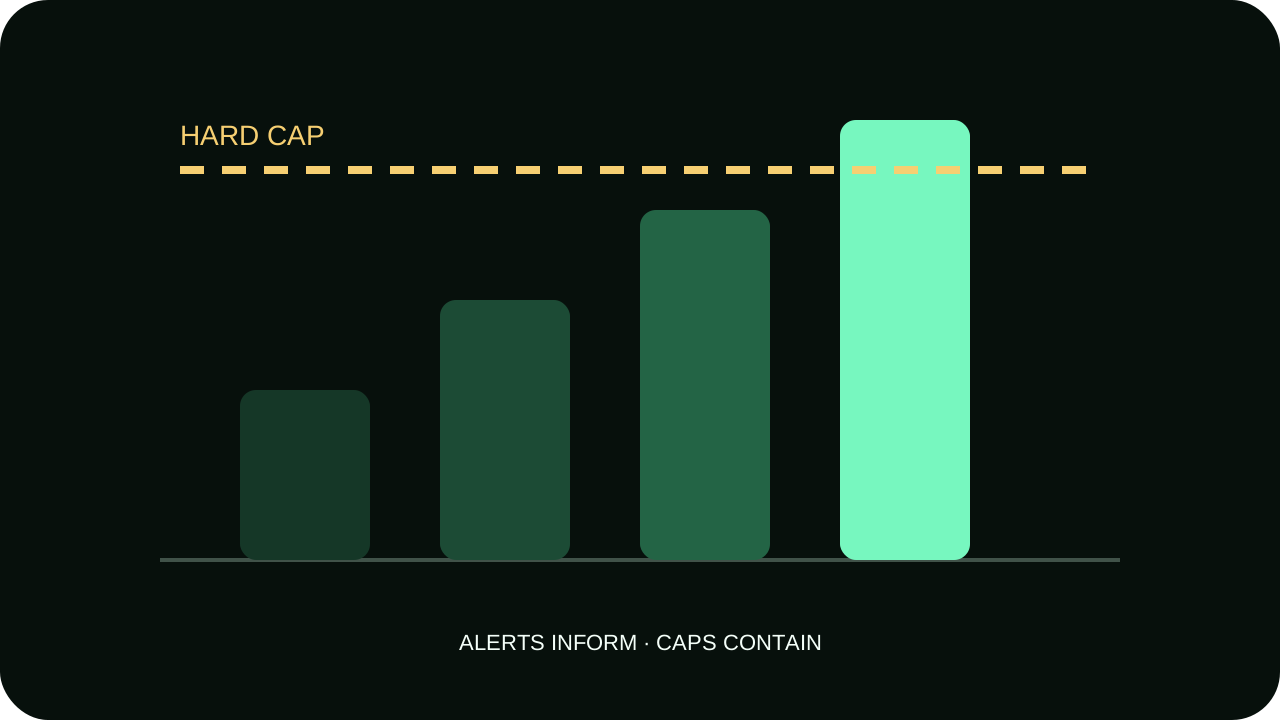
Model a conservative emergency buffer. This does not replace provider billing data, but it makes an alert-only setup visible.
PUBLIC EVIDENCE
We do not claim every provider lacks controls. Google introduced spend caps and tightened unrestricted keys; self-hosted alternatives exist. The gap is consistent, low-ops protection across providers.
HONEST LIMITS
It detects risky patterns and configuration gaps, not live account activity.
Masking a key in code is not enough. Revoke it at the provider.
Provider limits, delays and account behavior change. Verify them directly.
Run the local scan now. Monitoring automation is in private beta and is not accepting payments yet.
No. The check runs in your browser and nothing you paste is transmitted to us. Never paste a live secret into any website, including this one — redact it first.不需要。检查在你的浏览器里运行,你粘贴的任何内容都不会传给我们。永远不要把生效的密钥粘进任何网站,包括本站——先脱敏。
Whether keys appear in client-reachable code, whether provider-side restrictions and spend caps are configured, and whether a leak would be noticed before billing closes.密钥是否出现在客户端可触及的代码里、供应商侧的限制与花费上限是否配好,以及一旦泄露能否在账单结算前被发现。
Yes. There is no paid tier on this tool.免费。这个工具没有付费档。